HPE Patched 72 Flaws in the Wi-Fi OS Behind Its 139% Rally
Eight of the flaws carry the maximum severity score and are reachable over a network with no credentials. The division's president sold $2.0 million of stock the day before the bulletin, under a plan set months earlier. The open question is whether enterprise Wi-Fi buyers start pricing a vendor's patch record.
 Richard Tang · 4 min read
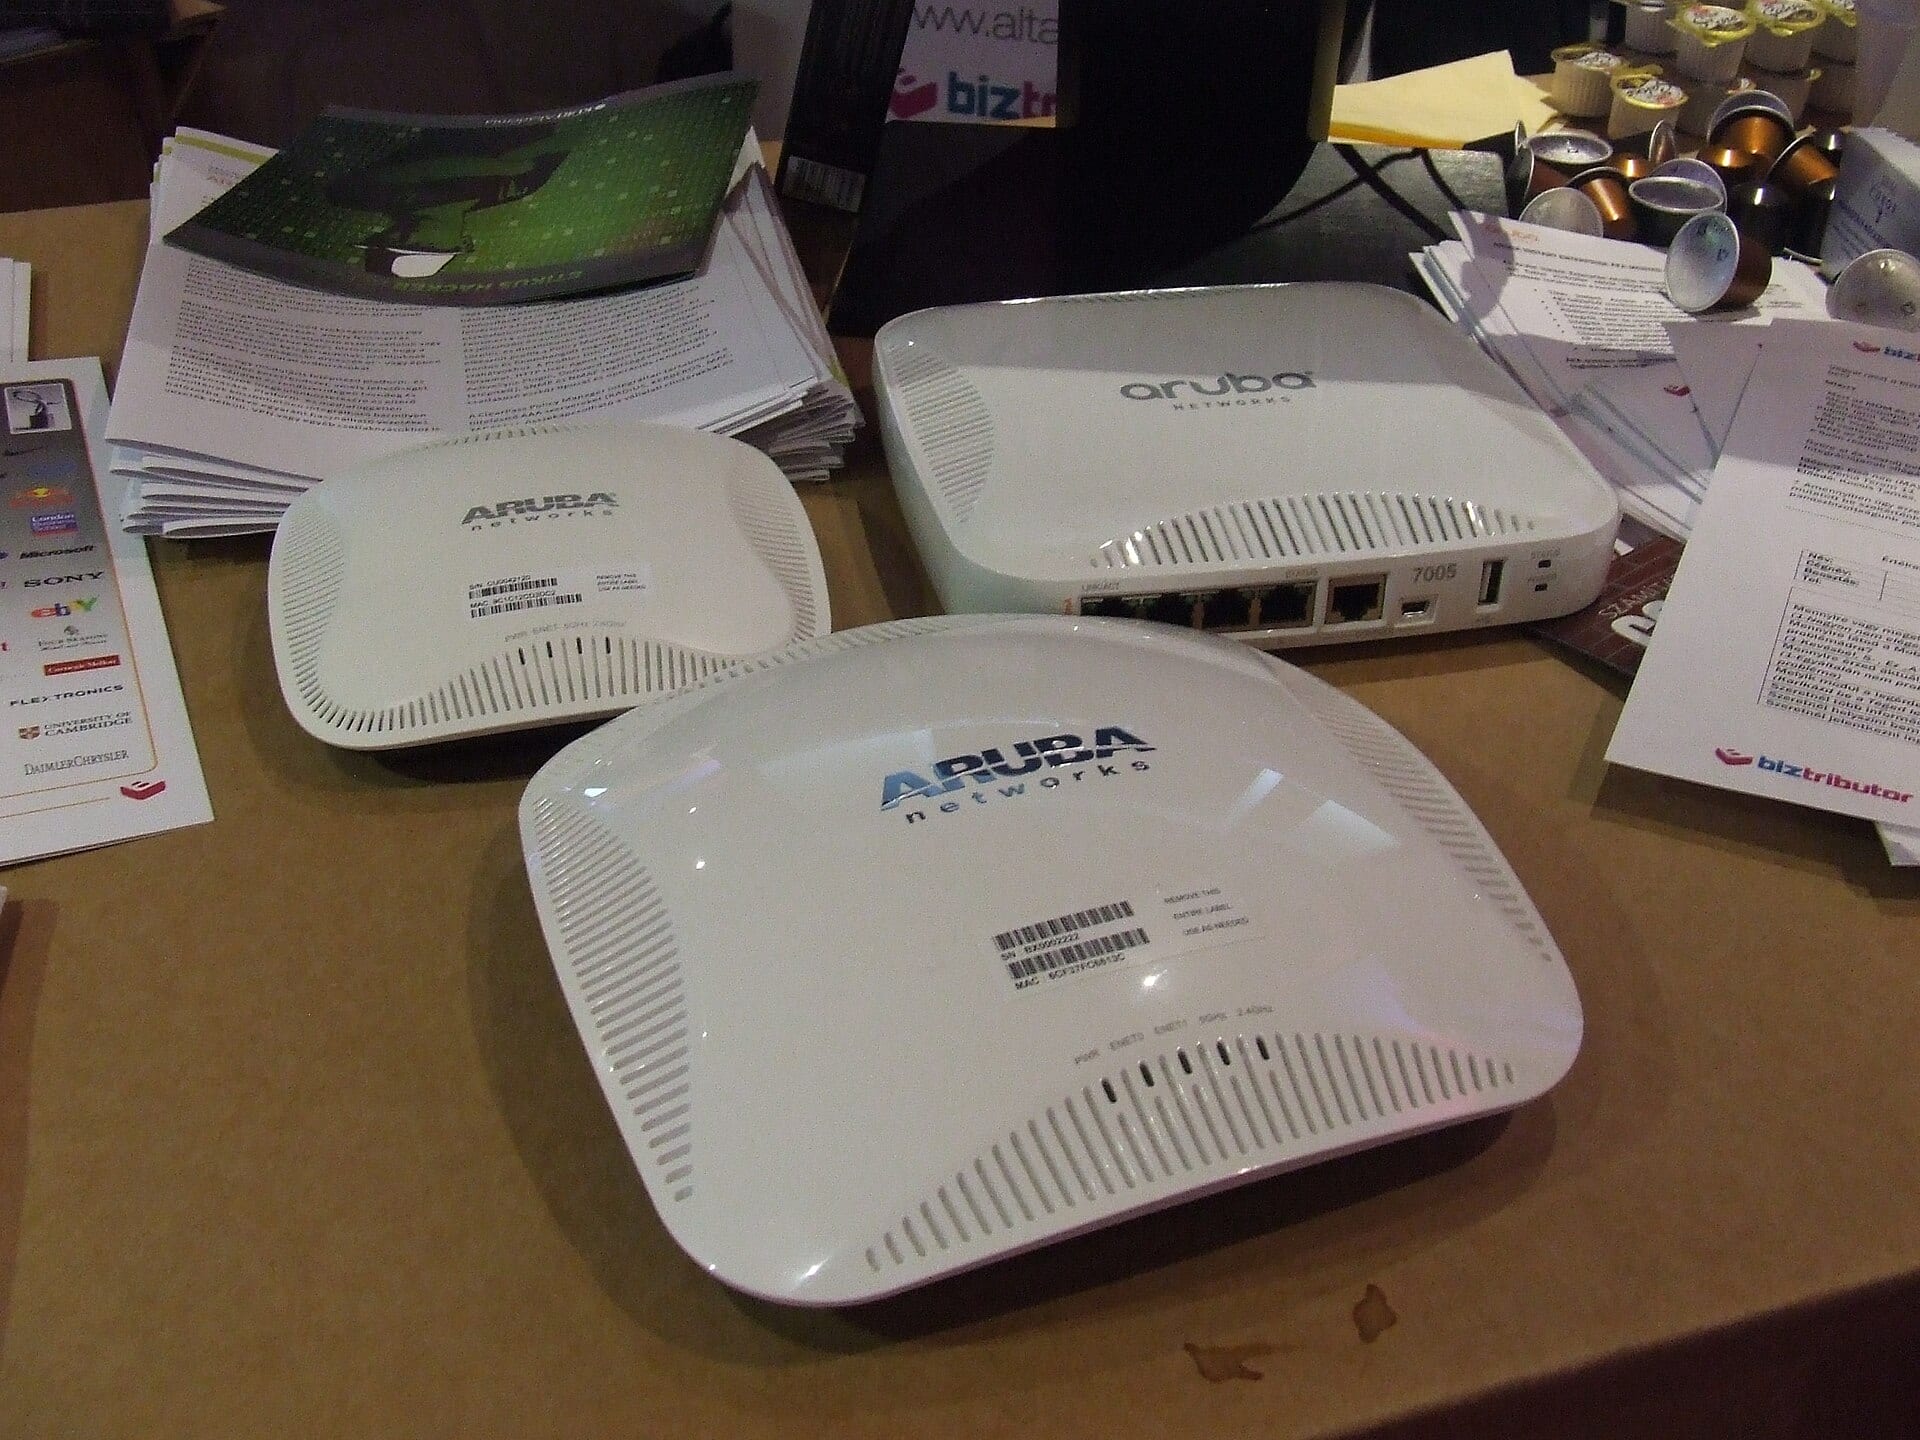
Hewlett Packard Enterprise+2.04% — Hewlett Packard Enterprise, up 2.04 percent today (HPE) has gained 139% this year, and the rally rests on one division: networking, assembled from the Juniper acquisition after the Justice Department settled its challenge in June 2025 12. On October 22 that division shipped a patch batch HPE had flagged a week in advance as "larger than usual": 72 vulnerabilities in ArubaOS, the operating system that runs the Wi-Fi controllers, gateways and access points inside enterprises 34.
HPE says it has seen no public exploit code and no sign the flaws are being used, and none of the 72 was in the known-exploited catalog kept by the Cybersecurity and Infrastructure Security Agency (CISA) as of October 23 34. That record does not itself threaten the rally. What the week tests is whether the people who buy enterprise Wi-Fi start weighing a vendor's patch record alongside price and performance.
HPE has left both market benchmarks far behind this year
Data
| Value | |
|---|---|
| HPE | 138.8% |
| QQQ | 14.9% |
| S&P 500 | 12% |
The flaws are dormant, in the layer attackers are hitting hardest
Eight of the 72 carry the maximum 10.0 score: authentication bypasses that end in remote code execution, plus unauthenticated SQL injection, command injection and buffer overflows 4. All are reachable over a network with no privileges and no user interaction, and CISA's assessment of the headline flaw rates the attack automatable and the technical impact total, with exploitation so far as none 3.
That quiet has not lasted elsewhere this autumn. The infrastructure flaws exploited fastest sat in management consoles, the software that configures network gear and holds its credentials; Cisco's+1.63% — Cisco, up 1.63 percent today firewall-management and identity-engine flaws were exploited in the days around their September disclosure 6. ArubaOS's weak spots sit in the same layer: the web management interface, the command line and PAPI, the protocol its access points speak 3. HPE shipped a comparable batch of critical flaws in StoreOnce, its backup-appliance line, in June 2025, the second such drop inside 16 months 4.
Customers pay first; the president's sale was scheduled months ahead
The first bill lands on customers running end-of-maintenance releases, versions HPE no longer updates: the bulletin lists no fix for them, only an instruction to move to a supported branch 3. Everyone else spends an emergency patch week, with management interfaces locked to trusted network segments until it is done 3.
Rami Rahim, who ran Juniper and now leads HPE Networking, sold $2.0 million of stock on October 21, the day before the bulletin 5. His trading plan was adopted on June 30, months before HPE's October 15 advance notice existed, and he kept the large majority of his holding 5. The dates describe an ordinary scheduled sale. The governance line that does move is lobbying: HPE's bill rose by about a third in a quarter, to $1.83 million, while Democratic senators press the Justice Department's inspector general over the settlement 2.
Concentration protects the vendor and slows the buyer
The complaint the Justice Department settled argued that HPE-Juniper, alongside Cisco, would control more than 70% of the United States enterprise wireless LAN market 2. A buyer with few alternatives is more likely to absorb the patch week than to punish the vendor for it. That insulation is what lets a patch record like this one coexist with this year's run.
HPE's quarterly revenue stepped up once Juniper consolidated
Data
| Quarterly revenue | |
|---|---|
| FQ4 '24 | $8.46B |
| FQ1 '25 | $7.85B |
| FQ2 '25 | $7.63B |
| FQ3 '25 | $9.14B |
| FQ4 '25 | $9.68B |
| FQ1 '26 | $9.3B |
| FQ2 '26 | $10.68B |
| FQ3 '26 | $12.21B |
Demand itself is not in question. At HPE's networking investor day on September 30, campus and branch Wi-Fi, the office and remote-site networks this bulletin touches, was put at roughly half of networking revenue, with orders growing 3.5 times faster than revenue 7. Rahim said from the same stage that some customer equipment "belongs in a museum," in a session where analysts argued AI now finds flaws faster than vendors patch them 7.
What would turn software quality into a price
HPE has raised its free-cash-flow target for the next fiscal year to at least $5 billion, and its fiscal fourth-quarter results, due in December, will show whether margins hold 1. The shorter list sits with CISA: any of the eight crossing into the known-exploited catalog would hand procurement teams a documented reason to write patch cadence into contracts 3.
Demand has carried the stock this far. The catalog is the first place evidence to the contrary could appear.
Get Security by email, free
The breaches, flaws and security vendors AI is putting to the test. In our daily email, every weekday.