Rapid7 counted AI in 8% of incidents as CrowdStrike rose 6% on Nvidia's agent-security list
Security stocks re-rated on Nvidia's agent-security partner list in the same 48 hours Rapid7's Q3 telemetry put AI inside 8 percent of tracked incidents, with humans still choosing every target. The threat actually on the wire showed up in PHP: two unauthenticated code-execution flaws probed four days before they were disclosed.
 Vincent Jiang · 3 min read
The partner list moved the money, the telemetry did not
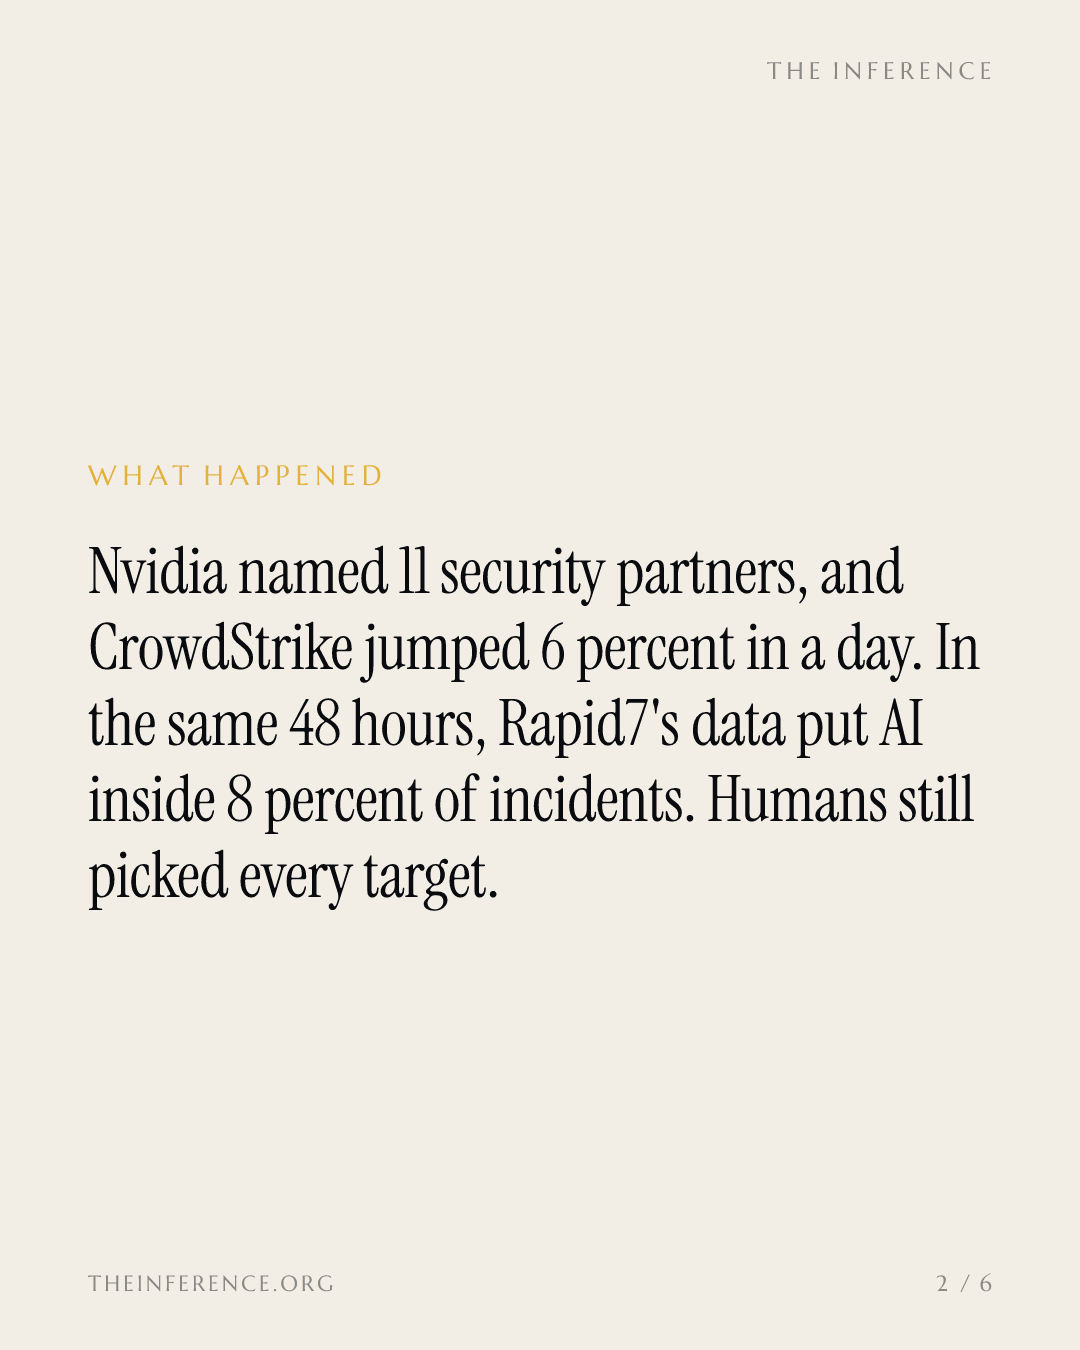
On October 21, CrowdStrike−0.39% — CrowdStrike, down 0.39 percent today rose 6 percent to $241.02 after Nvidia−3.90% — Nvidia, down 3.90 percent today named 11 security partners for its OpenShell agent architecture at GTC Berlin, a list with no dollar terms attached, and the security complex rose as much as 8.3 percent in the session 10. Datadog−3.68% — Datadog, down 3.68 percent today gained 6 percent and Okta−2.32% — Okta, down 2.32 percent today 4 percent, gains one trading desk called expectation-driven until adoption data arrives 9.
The agent-security list re-rated the security complex in one session
Data
| Value | |
|---|---|
| CrowdStrike | 6 |
| Datadog | 6 |
| Okta | 4 |
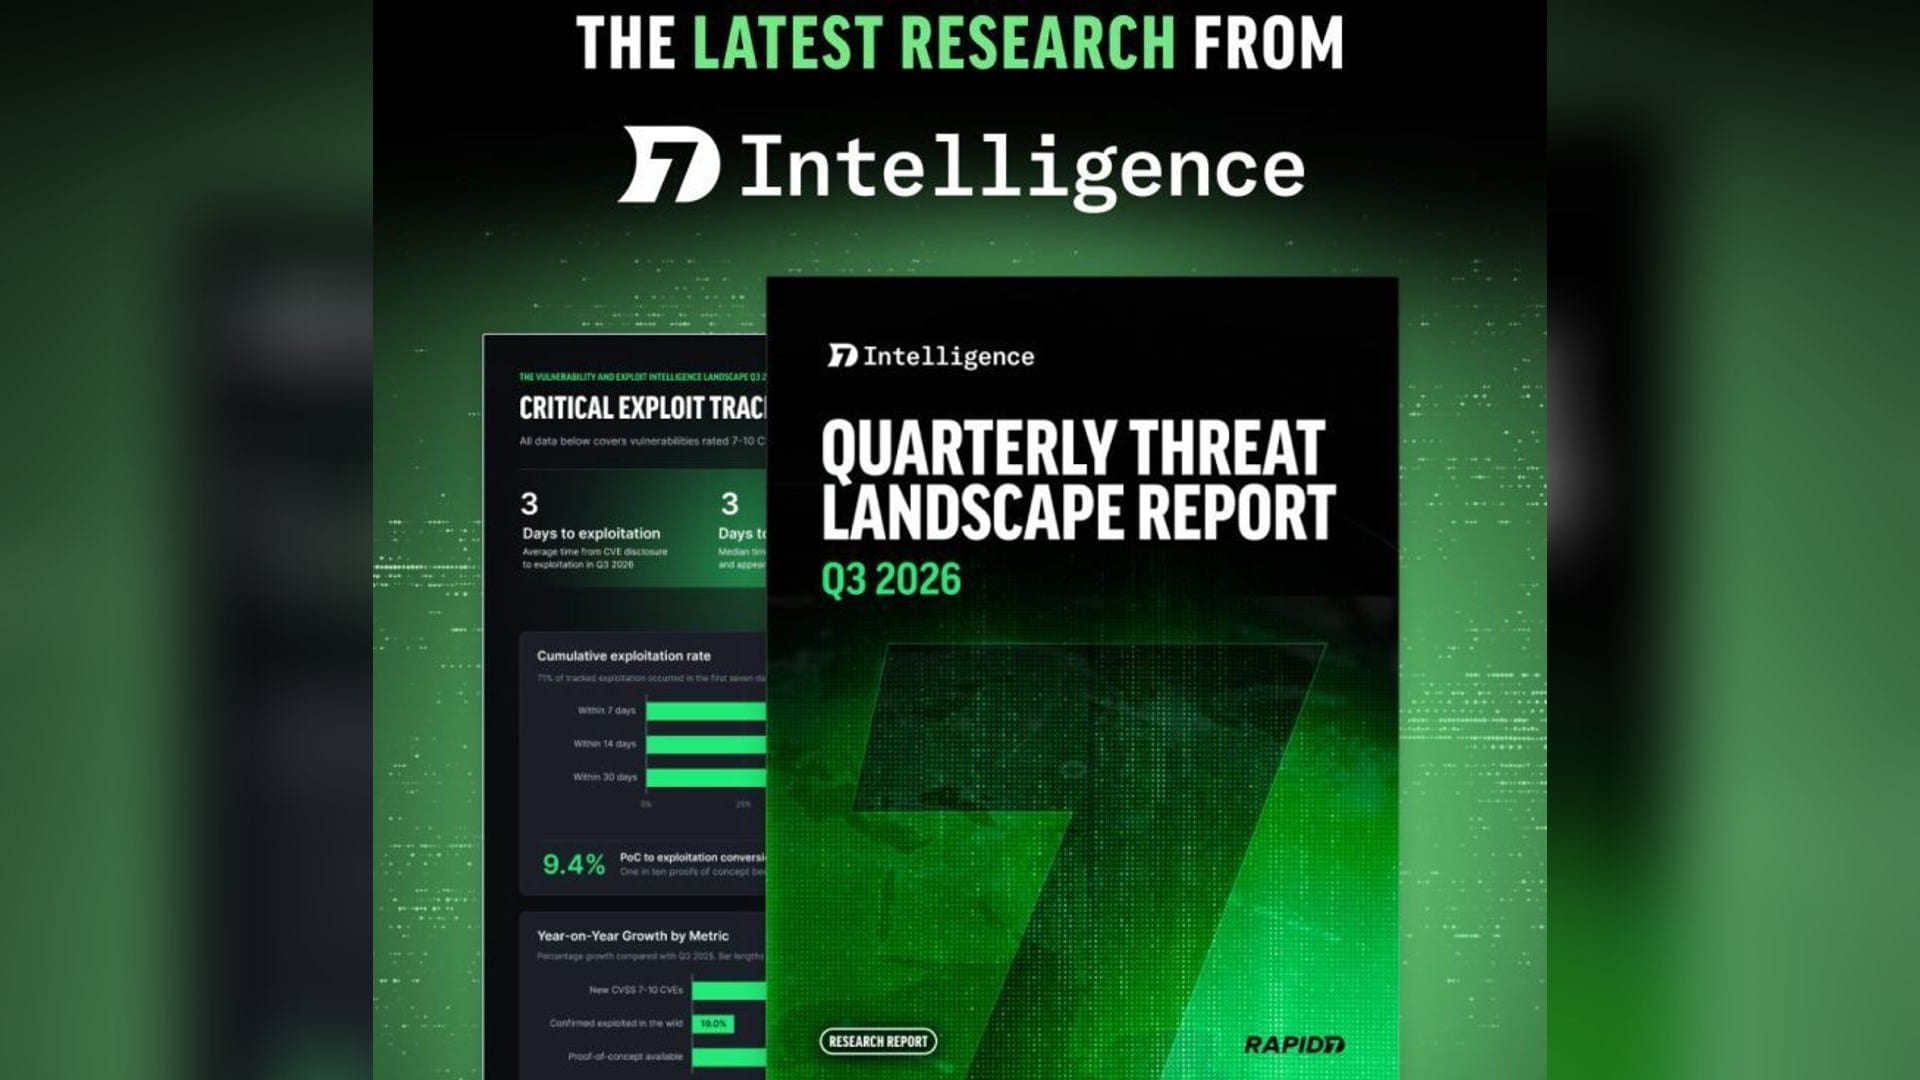
The same 48 hours delivered Rapid7's+4.66% — Rapid7, up 4.66 percent today Q3 2026 Quarterly Threat Landscape Report, drawn from the company's own incident-response telemetry: AI was an operational component in 8 percent of tracked incidents, and a human still chose the target in every documented case 15. "The board-deck version of this year has been wall-to-wall AI attackers, and the data doesn't support that story," said Douglas McKee, Rapid7's director of vulnerability intelligence 5.
What attackers actually did in Q3
High-severity vulnerabilities were exploited an average of three days after disclosure, 71 percent inside the first week, and 79 percent needed no authentication and no user interaction, the class Rapid7 calls "holy grail": a door that opens without a login or a click 15. Ransomware stayed human-run at scale, with 1,112 US leak-site listings, roughly eight times Germany's, and two brands in a dead heat 15. High-severity disclosures rose 133 percent year over year, and one in ten public proofs of concept became a working attack within 30 days 2.
Two ransomware brands claimed more incidents than the next three combined
Data
| Value | |
|---|---|
| The Gentlemen | 342 |
| Qilin | 339 |
| INC Ransom | 99 |
| DeadLock | 98 |
| KryBit | 95 |
PHP showed the real shift: speed, not autonomy
The live counterexample landed the same day. PHP shipped emergency fixes on October 21 for CVE-2026-109618 and CVE-2026-109619, two CVSS 9.2 unauthenticated remote-code-execution flaws in the runtime behind almost 70 percent of websites, and an update is the only complete remediation 378.
Amazon's−4.08% — Amazon, down 4.08 percent today MadPot honeypot logged the first exploitation attempt on October 17, four days before disclosure and while the flaws were under embargo 67. Cloudflare counted thousands of attempts in the 10 hours before the release and millions since, and about one million of 2.6 million internet-facing PHP hosts run versions that no longer get fixes 67.
Amazon CISO CJ Moses named the mechanism: AI-assisted analysis makes it cheaper to turn a patch diff into a working exploit, letting more actors move "within hours or even minutes" 7. Rapid7's own vice president of intelligence, Christiaan Beek, calls the 8 percent "a snapshot of adoption, not a ceiling" 1.
The vendor at the bottom of its range
The company that measured all this closed at $13.22 on October 19, in a 52-week range of $4.97 to $19.84, with insiders net buyers of $3.8 million and a 56-of-100 GuruFocus quality score flagged as a possible value trap 4. Revenue growth has slid from 13.1 percent to negative across twelve quarters 11. The Intelligence unit that shipped same-day detection for GitLab's 10.0 flaw on October 13 10 faces its own test on November 4, when Rapid7 reports third-quarter results 1.
Rapid7's growth slid for twelve straight quarters, into decline
Data
| Revenue growth, YoY | |
|---|---|
| Q3 '23 | 13.1% |
| Q4 '23 | 11.3% |
| Q1 '24 | 12% |
| Q2 '24 | 9.2% |
| Q3 '24 | 8% |
| Q4 '24 | 5.4% |
| Q1 '25 | 2.5% |
| Q2 '25 | 3% |
| Q3 '25 | 1.5% |
| Q4 '25 | 0.5% |
| Q1 '26 | -0.3% |
| Q2 '26 | -1.5% |
This week's premium accrued to the names attached to the agent story. The attacker already here works in three days and needs no password.
Get Security by email, free
The breaches, flaws and security vendors AI is putting to the test. In our daily email, every weekday.